“Which Docsie workspaces can you see, and what's in my default one?”
- list_workspaces
- get_workspace_overview
Only the workspaces your own account can view, in the organization you picked at sign-in.
Docsie MCP server · Security and team agents
Each person connects through OAuth with their own Docsie account and reaches only what that account can already see. For an agent many people share, an admin creates a service token tied to one workspace. Either way, only the permission packs you tick are exposed.
On every Docsie plan, Free included. MCP tokens are bearer tokens, so treat them like passwords.
https://app.docsie.io/mcpWorks in Claude, ChatGPT, Claude Code, Cursor, Codex and any MCP client.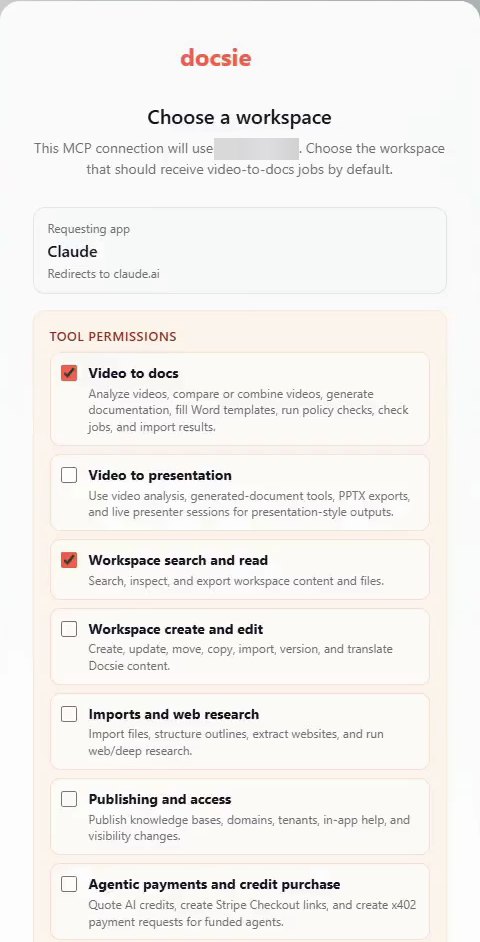
The Docsie screen Claude sends you to when you connect. Choose the default workspace, then tick the tool permissions. Here Video to docs and Workspace search and read are ticked; Workspace create and edit and Publishing and access are not.
What you can ask
Example requests and what the scoping does with them. A personal sign-in sees what that person can see; a service token sees one workspace.
“Which Docsie workspaces can you see, and what's in my default one?”
Only the workspaces your own account can view, in the organization you picked at sign-in.
“Find our VPN setup steps in the onboarding docs and fix the outdated one.”
With only Workspace search and read ticked, it can find and read the article but can't change it.
“Turn this week's training recordings into guides.”
The jobs run in the token's one workspace, and the usage is billed to the organization that owns the token.
How it works
Each person adds https://app.docsie.io/mcp and signs in with OAuth 2.1 and PKCE. Most clients register themselves. For hosts that can't, an admin registers a client ID with its redirect URIs.
On Docsie's sign-in screen, choose the default workspace and tick the packs. Video to docs, Workspace search and read, and Remote Docsie agent runs are on by default.
For a team bot, an admin creates a service token in MCP Access with one workspace and the packs it needs. Copy it right away, because it's shown once.
Permissions and limits
Workspace create and edit, Video to presentation, Imports and web research, Publishing and access, and Full Docsie workspace agent stay off until you tick them.
Connecting works on every Docsie plan. AI jobs use the organization's AI credits, and a service token's usage is billed to the organization that owns it.
Revoke a connection or a service token whenever you need to. If a token leaks, revoke it at app.docsie.io/mcp/oauth/revoke/ and connect again.
Docsie security →FAQ
Each connection is scoped five ways: the person who authorized it, one Docsie organization, a default workspace, the workspaces that person is a member of, and the packs that were ticked.
No. They reach only the workspaces your own account can view, in the organization you chose at sign-in. The workspace you pick is the default target.
Yes. Tick only Workspace search and read. Your assistant can search, read and export docs but can't create, edit or delete anything.
An admin creates one in MCP Access for a single workspace and the packs it needs. It's shown once, can be revoked at any time, and its usage is billed to the organization.
OAuth 2.1 with PKCE. Clients that support dynamic client registration register themselves. For others, an admin registers a stable client ID with its redirect URIs.
MCP tokens are bearer tokens, so anyone holding one can use it. Revoke it at app.docsie.io/mcp/oauth/revoke/ and connect again.
Docsie MCP server
Connect people with their own sign-in, give shared agents a scoped token, and tick only the packs each one needs.